The Cyber Resilience Act Timeline: Every Date, What It Means, and Who It Hits
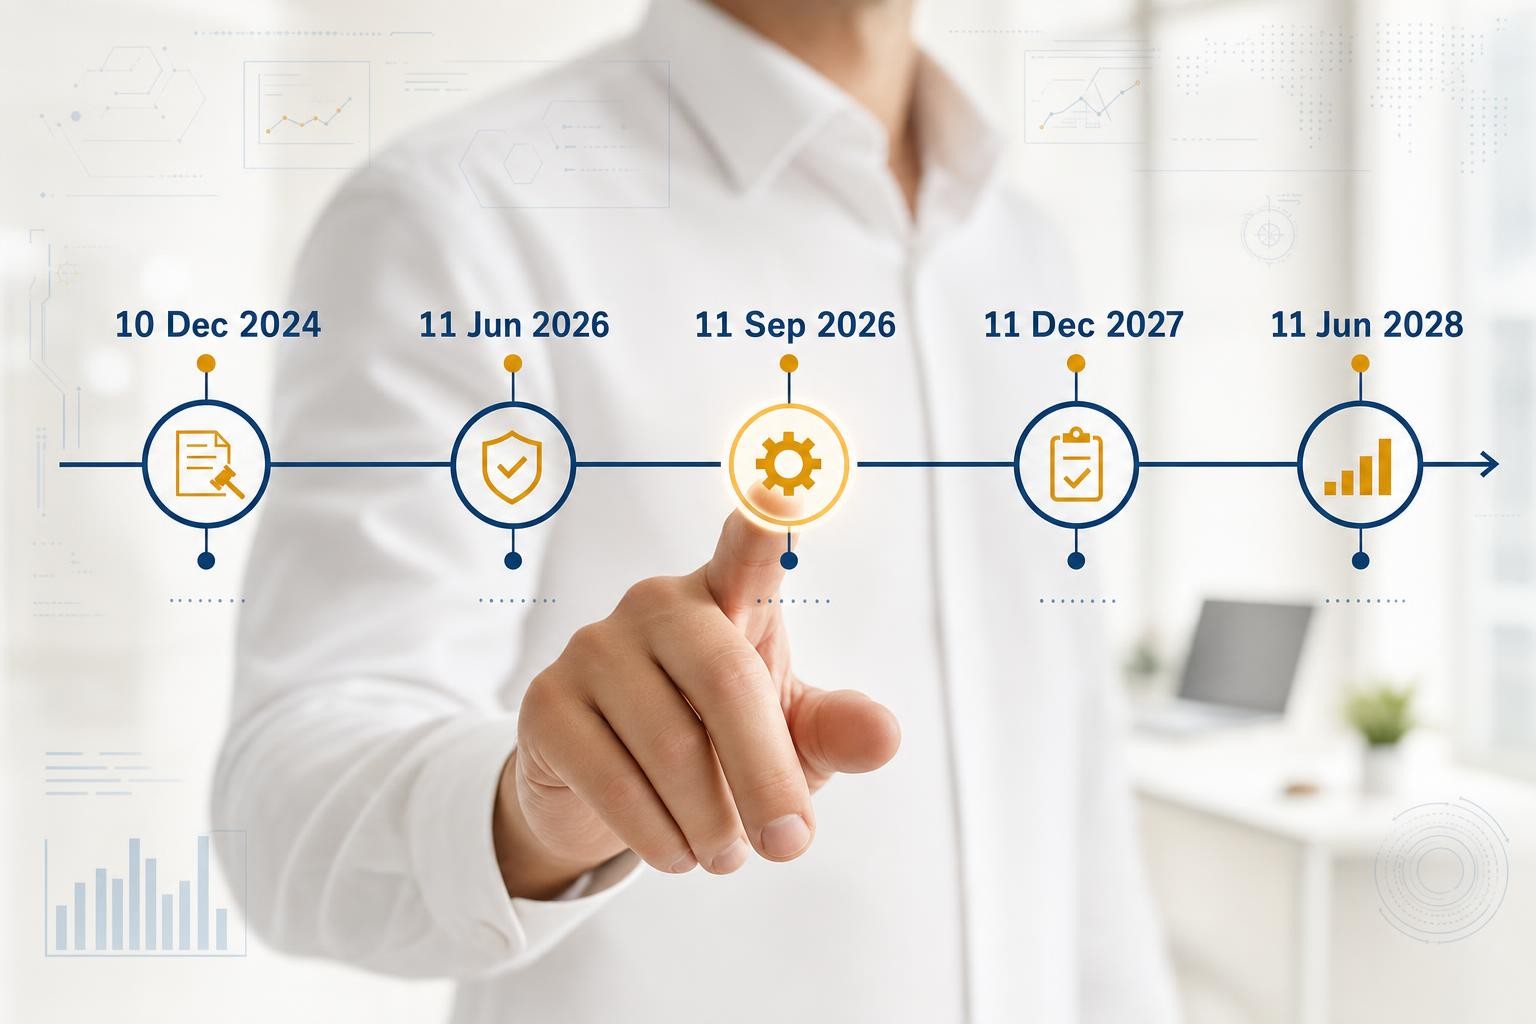
There are five dates that matter in the Cyber Resilience Act timeline. One started the clock (10 December 2024). Three impose actual obligations - 11 June 2026 (conformity assessment infrastructure), 11 September 2026 (manufacturer reporting), and 11 December 2027 (full product compliance). One is a run-off for existing certificates (11 June 2028). Everything else is still in motion.
This article provides general guidance on the Cyber Resilience Act, not legal advice. Confirm specifics against Regulation (EU) 2024/2847.
Key points
- The CRA is already partially in force. Two of the three obligation dates have already passed.
- 11 September 2026 is live. Article 14 reporting obligations apply now. If you make or maintain a product with digital elements sold in the EU, you are in scope - even if your product was placed on the market years ago.
- 11 December 2027 is when the full product compliance regime - essential requirements, conformity assessment, CE marking - becomes enforceable.
- No CRA harmonised standard has yet been cited in the Official Journal. The presumption of conformity under Article 27 is not yet available for any product category.
- The Digital Omnibus proposal (November 2025) does not move any CRA date. It is a separate legislative proposal.
The Cyber Resilience Act timeline at a glance
| Date | What applies | Who it hits | Status |
|---|---|---|---|
| 20 November 2024 | Regulation (EU) 2024/2847 published in the Official Journal | - | Done |
| 10 December 2024 | CRA enters into force; clocks start | All in-scope economic operators | Done - no obligations yet |
| 11 June 2026 | Chapter IV: notifying authorities and notified bodies can be designated | Member States; conformity assessment bodies | Done - infrastructure on |
| 11 September 2026 | Article 14: reporting obligations apply | All manufacturers of products with digital elements on the EU market | Live |
| 11 December 2027 | Full application: essential requirements, conformity assessment, CE marking | All in-scope manufacturers, importers, distributors | Upcoming |
| 11 June 2028 | Run-off: existing EU type-examination certificates and approval decisions expire (unless earlier) | Manufacturers holding pre-CRA certificates | Run-off, not a new obligation |
10 December 2024 - Entry into force
The Cyber Resilience Act, Regulation (EU) 2024/2847, entered into force on 10 December 2024[1]. Nothing became obligatory on that date. The regulation was published in the Official Journal on 20 November 2024, and entry into force followed twenty days later.
What it means in practice: The clock started. Transition periods began running. Manufacturers who had been tracking the draft text could now plan against firm dates. No product needed to change, no report needed to be filed.
11 June 2026 - Chapter IV: conformity assessment infrastructure
Chapter IV (Articles 35 to 51) applies from 11 June 2026[2]. Chapter IV covers the notification of conformity assessment bodies - the third-party auditors that Class II and Critical product manufacturers must use, and that any manufacturer may use in the absence of harmonised standards.
From this date, Member States are required to have their procedures in place for assessing, designating, and notifying conformity assessment bodies. Bodies can now be formally designated and listed in the Commission's database.
What it means in practice: The notified-body machinery switched on before the harmonised standards that would normally feed it existed. For manufacturers of Class II or Critical products, this matters: a notified body is mandatory for them regardless of what happens with standards. For Class I manufacturers, it means third-party assessment is available as a route even now - but capacity at notified bodies is limited, and the queue is forming. See our post on CRA conformity assessment and notified bodies for the current state of play.
11 September 2026 - Article 14 reporting obligations
This is the most misread date in the entire CRA timeline. Read this section carefully.
Article 14 of Regulation (EU) 2024/2847 applies from 11 September 2026, more than 15 months before the main body of the CRA.[3]
From this date, manufacturers of products with digital elements must report two categories of event via ENISA's Single Reporting Platform (SRP):
- Actively exploited vulnerabilities - a vulnerability in your product for which there is reliable evidence of active exploitation in the wild.
- Severe incidents - incidents having a significant impact on the security of the product.
The reporting clock runs as follows:
| Stage | Deadline | Content |
|---|---|---|
| Early warning | 24 hours from awareness | Notification that an event has occurred |
| Vulnerability/incident notification | 72 hours from awareness | Technical detail on the event |
| Final report (actively exploited vulnerability) | Within 14 days of a corrective measure being available | Root cause, corrective measures, preventive actions |
| Final report (severe incident) | Within one month | Full account of the incident |
Reports go to ENISA and the coordinating CSIRT via the SRP. A single submission on the platform reaches both simultaneously - manufacturers do not need to notify multiple national authorities separately.
ENISA's Single Reporting Platform is scheduled to be operational from 11 September 2026, the same date the mandatory reporting obligations begin.[4]
The critical point most manufacturers miss
Article 14 reporting obligations apply to all products with digital elements already on the EU market, not only to products placed on the market after 11 September 2026. A router shipped in 2022, firmware distributed before the CRA existed, software installed across European enterprises for years - all of it is in scope from 11 September 2026 if it falls within the CRA's product definition.
If you have been planning your CRA programme around the 2027 date, this is the obligation that is already live. For a detailed breakdown of what Article 14 requires and how to prepare, see our post on the 11 September 2026 reporting deadline, and the Article 14 trigger guide for deciding whether a given event is reportable.
11 December 2027 - Full application
The main provisions of Regulation (EU) 2024/2847 apply from 11 December 2027. This is the date that most CRA compliance programmes are built around, and it is the correct anchor for product conformity work.
From this date, all in-scope products placed on the EU market must:
- Meet the essential cybersecurity requirements in Annex I (both security-by-design requirements and vulnerability handling requirements).
- Have completed the appropriate conformity assessment route - self-assessment for most Default class products, notified body involvement for Class II and Critical products.
- Have technical documentation prepared in accordance with Annex VII.
- Carry an EU Declaration of Conformity signed by the manufacturer.
- Bear CE marking.
This applies to products placed on the market from 11 December 2027. Products already on the market before that date are not required to be withdrawn, but Article 14 reporting obligations apply to them from 11 September 2026 regardless.
What it means in practice: Work backwards from 11 December 2027. Conformity assessment for Class II and Critical products - particularly where a notified body is involved - takes months. Technical documentation must be complete before the DoC is signed. Risk assessments under Article 13 underpin the whole structure. The CRA compliance checklist and readiness roadmap sequences these steps.
11 June 2028 - Run-off for existing certificates
This date is often misread as a new obligation. It is not.
EU type-examination certificates and approval decisions issued in respect of cybersecurity requirements under pre-CRA frameworks remain valid until 11 June 2028, unless they expire earlier. After that date, they lapse. Manufacturers holding such certificates should plan their transition to CRA-compliant conformity assessment routes before that deadline - but the deadline itself creates no new positive obligation.
Dates that are not yet fixed
Several things that matter to CRA compliance do not yet have firm dates. Label them accordingly in your planning.
Harmonised standards
As of September 2026, no CRA harmonised standard has been cited in the Official Journal of the EU. Until a standard is cited under Article 27, it does not confer the presumption of conformity. This matters because the presumption of conformity is the main mechanism by which manufacturers demonstrate that their products meet the essential requirements without a notified body assessment.
On 13 August 2026, ETSI opened the Public Enquiry on 17 vertical final draft European Standards covering Annex III product categories.[5] The approval procedure runs until mid-September to mid-November 2026 depending on the vertical, and final versions are expected around December 2026. Citation in the Official Journal would follow after that - and is not guaranteed to any specific date.
The horizontal standards developed by CEN-CENELEC are on a separate track, with the generic security requirements part scheduled later still - in part after the main CRA application date.
For the current state of the standards landscape, see our post on CRA harmonised standards and the presumption of conformity, and the breakdown of the 17 ETSI vertical drafts.
Delegated and implementing acts
The Commission is still developing several delegated and implementing acts under the CRA, including the technical description of the categories of important and critical products under Annexes III and IV, and any scheme linking European cybersecurity certification to CRA conformity. Do not assign firm dates to these beyond what is publicly confirmed.
The Digital Omnibus proposal
On 19 November 2025, the European Commission unveiled the Digital Omnibus legislative package. Among its proposals is an ENISA-operated Single Entry Point for cybersecurity incident reporting - a unified portal that would allow entities to satisfy reporting obligations under NIS2, GDPR, DORA and other frameworks through one submission.
This is a proposal. It is not yet law. It does not move any CRA date. The CRA's own Single Reporting Platform is separate infrastructure. The Digital Omnibus Single Entry Point, if adopted, would build on it - but the legislative process is still running, and the platform itself is expected 18-24 months after the relevant regulation would enter into force.
How to read the timeline backwards from your own product
The right way to use this timeline depends on where your product sits today.
If your product is already on the EU market: Article 14 reporting obligations apply to you from 11 September 2026. Set up your reporting process, register on ENISA's SRP, and designate an authorised reporter. This is not a 2027 problem.
If you are planning a new product launch before 11 December 2027: You are not required to meet the full essential requirements before that date. But you should be building to them now, because the conformity assessment work - especially for Class II and Critical products - takes time that you may not have if you wait.
If you are planning a new product launch on or after 11 December 2027: Work backwards. Allow time for:
- Risk assessment and technical documentation (Article 13, Annex VII)
- Conformity assessment (weeks to months depending on class and route)
- EU Declaration of Conformity and CE marking
- Any notified body involvement (book early - capacity is limited)
The CRA compliance checklist sequences these steps. The scope checker helps you confirm whether your product is in scope and which class it falls into. The deadlines reference gives you a quick summary to share with your team.
Related reading on CRA Facts
- What the 11 September 2026 CRA reporting deadline means for you - the Article 14 obligations in full detail
- Your CRA compliance checklist: a sequenced readiness roadmap - what to do and in what order
- CRA harmonised standards and the presumption of conformity - where the standards landscape stands
- CRA conformity assessment in 2026: notified bodies are open, but the standards aren't ready yet - the practical state of third-party assessment
- Is my product in scope? - use the scope checker to confirm your product class
- CRA deadlines at a glance - the quick-reference summary
- Regulation (EU) 2024/2847 (Cyber Resilience Act) | EUR-Lex
- The Cyber Resilience Act - Summary of the legislative text | European Commission
- Cyber Resilience Act - Reporting obligations | European Commission
- Single Reporting Platform (SRP) | ENISA
- ETSI launches approval process for 17 European Standards supporting the Cyber Resilience Act
Related reading
Three Weeks Into CRA Reporting: What Early Users Learned and What a "Disclosure Delay" Really Means
Article 14 reporting has been live for three weeks. Here is what early users of ENISA's Single Reporting Platform report, what a "disclosure delay" does and does not change, and the four things worth doing this week.
CRA SBOM Requirements: What Goes Inside, Which Format Versions to Use, and Where VEX Fits
The CRA says your SBOM must be machine-readable but not what fields it needs. Here is what goes inside, which CycloneDX and SPDX versions still count, and why VEX is optional.
Does the Cyber Resilience Act Require Penetration Testing?
The CRA never mentions penetration testing. Annex I, Part II, point 3 requires "effective and regular" security tests - here is what that means in practice.